This document will be up to date when there are formal necessities for ADOs here at CMS. A CKMS Apply Statement (CKMS PS) paperwork how key administration procedures and strategies are used to enforce the CKMS Safety Policy. The insurance policies outlined within the CMS IS2P2 assist assembly the requirements for controls that mandate CMS to establish a coverage and related procedures for managing information systems. Necessary limitationStrong algorithms can’t rescue weak key handling. Most real-world cryptographic failures are operational — keys in code, unrotated keys, misplaced keys that render data completely unreadable — not broken ciphers. Key protectionHardware-backed storage, least-privilege access, separation of duties for key operations, and audited utilization.
A firm operates two tugs, every towing three barges stuffed with coal for supply. En route, the tugs encountered a storm which sank the last barge of every tug’s tow. The evidence means that there was a climate report broadcast over radio which would have warned the tug-captains of the climate and persuaded them to place into harbor. Nevertheless, the tug-captains only had personal radio receiving units which have been broken and their employer did not https://wainscottpartners.com/whats-next-in-payments-sponsor-content-from-hexaware.html furnish them with sets for work.
- Swift revocation is essential for limiting the injury, stopping unauthorized entry, and maintaining the integrity of encrypted communications.
- The dynamic nature of knowledge security and privacy disciplines and the constant want for assessing threat throughout the CMS environment can outcome in gaps in policy, outside of the routine coverage evaluate cycle.
- Human error is often liable for compromised keys, and, while such problems can be avoided (to some extent) via automated solutions, coaching is also necessary.
- Otherwise, exterior users must submit personal key restoration requests.
- A specific particular person or service account that’s responsible for the key’s lifecycle.
- The keys are used to encrypt and decrypt information both in transit and at rest.
Emea Compliance
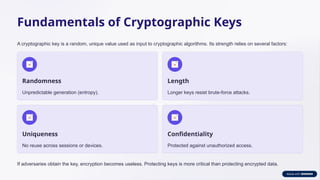
Simplify lifecycle monitoring, renewal, and compliance with our end-to-end encryption and PKI administration platform. This ought to be completed by encrypting (“wrapping”) the key underneath a pre-shared transport key (a key encryption key, or KEK), which may be either symmetric or asymmetric. A key is essentially only a random quantity – the longer and extra random it is, the more difficult it’s to crack.
Due To This Fact, it is important that the applying incorporate a safe key backup functionality, especially for applications that support data-at-rest encryption for long-term information shops. Keys or secrets and techniques ought to be shared out of band and should by no means be sent with or alongside the data the secrets or keys they’re protecting. Additionally, secrets and techniques shared out-of-band ought to be protected and not stored someplace that can be easily compromised (like on a piece of paper on a user’s desk).
Tier 3: Secrets And Techniques Supervisor (delivered To Applications)
In contrast, the asymmetric encryption model permits for freely sharing the basic public key, with the personal key strictly managed and protected by the important thing pair proprietor. A belief retailer is a repository that incorporates cryptographic artifacts like certificates and personal keys which may be used for cryptographic protocols corresponding to TLS. With effective cryptographic key administration, data that’s encrypted can still be protected even in the event of a breach, since encrypted information can’t be decrypted with out the right keys. Proper utilization of encryption and key administration will help an organization’s efforts to protect their information. NIST SP 800-57 Recommendations for Key Management (Part 1, Revision 5) supplies an updated guideline for basic cryptographic key administration. Requirements outline both functional and assurance necessities inside the CMS security and privacy environment.

This includes maintaining detailed records of who accessed the keys, when, and for what function, as well as implementing mechanisms to track and monitor key utilization. This stage of transparency and management strengthens the general safety of cryptographic key administration. Automation can make all of the difference, streamlining the encryption key lifecycle from technology and storage to rotation and deletion.
Regardless of business, today’s enterprises are more and more concerned within the enterprise of knowledge. By accumulating and analyzing related information, these organizations can acquire helpful insights that allow them to better tailor their products or services to meet the distinctive wants of their clients or customers. Gathering information also can streamline necessary processes corresponding to completing transactions on-line. Keys should by no means be saved alongside the info that they shield (e.g. on a server, database, and so forth.), as any exfiltration of the protected data is likely to compromise the key additionally. A single compromised key may lead to an enormous knowledge breach, leading to reputational harm, punitive regulatory fines, and a loss of investor and customer belief. This CMS information will use the term revoked key notification (RKN) to discuss with a mechanism to revoke keys.
Nist Special Publication 800-53 Revision 52Zero
Key storage determines how and where non-public keys are positioned. This performs a elementary position in elevating private key security. When using SSL/TLS certificates, public keys are printed inside the certificates itself, whereas personal keys may be saved in an encrypted format on exhausting drives or USB tokens. Strong passwords and entry control may help to safeguard these non-public keys. Additionally, encryption and correct key administration assist organizations meet crucial knowledge security regulations similar to GDPR, HIPAA, and PCI DSS, guaranteeing compliance whereas safeguarding sensitive information.
Destruction Methods By Storage Sort
We assist the world’s most critical industries protect, govern, and sustain trust across the whole spectrum. However once imported, keys are still non-exportable from every cloud. Once an encryption algorithm (such as RSA, ECC, or AES) is chosen, each key length and randomness play a crucial function in making certain knowledge stays protected in opposition to evolving cyber threats. The article also extends these obligations to certificates administration, requiring financial entities to maintain an up-to-date register and guarantee certificates are renewed earlier than they expire. Not only should the confidentiality and integrity of keys be protected, but in addition their availability.
In short, efficient key management is essential for making encryption work and preserving information techniques secure. Key management refers back to the processes and procedures involved in producing, storing, distributing, and managing cryptographic keys utilized in cryptographic algorithms to protect sensitive knowledge. It ensures that keys used to guard sensitive information are saved secure from unauthorized entry or loss. Good key administration helps keep the safety of encrypted info and is necessary for protecting digital property from cyber threats. Effective key management is essential for guaranteeing the confidentiality, integrity, and availability of encrypted information by securing cryptographic keys from unauthorized entry, loss, or compromise. There are several strategies for securely sharing keys, together with PKI, key administration systems (KMS), and hardware security modules (HSMs).