The number r is identified as “order” of the cyclic subgroup (the complete variety of all points in the subgroup). The Elliptic Curve Digital Signature Algorithm (ECDSA) is a variant of the Digital Signature Algorithm (DSA) which uses elliptic curve cryptography. Given knowledge is signed with an ECC personal key and signature verification is completed with an ECC public key. Signing given information utilizing ECDSA leads to different signatures when repeating the process, as a end result of the algorithm includes a random worth (k).
Recently, I am learning how Elliptic Curve Cryptography works. I searched across the internet, found so many articles and movies explaining it. Most of them are overlaying solely a portion of it, a few of them skip many critical steps how you get from here to there. In the tip, I didn’t discover an article that really explains it from end-to-end in an intuitive way. With that in thoughts, I want to write a post explaining Elliptic Curve Cryptography, cowl from the fundamentals to key change http://hotesib.ru/bestik/7b0LSPDVdaA/Airports-increasing-security-following-al-Qaeda-fears.html, encryption, and decryption. A faster strategy to multiplication is to use the double-and-add algorithm.

Double-and-add Algorithm
In addition, ECC requires less processing energy (CPU) and memory, resulting in significantly faster response occasions and throughput on Net servers when it’s in use. Performs a key trade operation using the supplied algorithm withthe peer’s public key. An elliptic curve private key for use with an algorithm such as ECDSA.
Elliptic Curve Area Parameters For Ecc
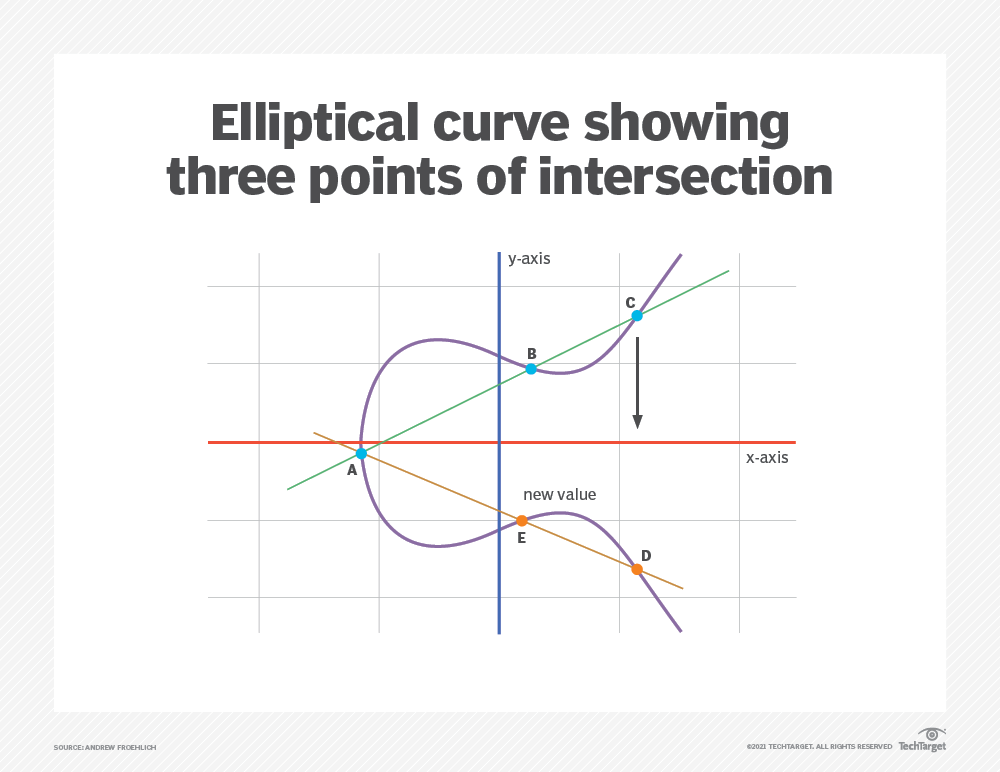
In this example, we will use an elliptic curve in the classical Weierstrass type. In the real world developers typically use curves of 256-bits or extra. A public EC key may be given in compressed type, which means that solely the X-value is supplied. The missing Y-value could be recalculated from the curve-ID (NID value), D, and X. In the upcoming operations, the inverse of a quantity is sometimes discovered mod p (modulo the prime number), and is typically discovered mod n (modulo the variety of factors on the curve).

Elliptic Curve Cryptography
- Then we take the odd and even from the above coordinates (according to the extra parity bit in the compressed representation).
- This key length offers adequate cryptographic security to keep hackers from cracking the algorithm.
- As A Outcome Of SSH2 is more secure, this distinction can influence validation selections between DSA vs RSA in sure environments.
- ECC crypto algorithms can use totally different underlying elliptic curves.
- Curves with a measurement of less than 224 bits shouldn’t be used.
Nevertheless, while the magic behind RSA and pals could be easily explained, is extensively understood, and rough implementations may be written quite easily, the foundations of ECC are nonetheless a thriller to most. In libica, an ECDSA signature has always a good size, and r is given by the primary half, and s by the second half of the signature. In some cases, for instance, using the secp521 curve, r or s might have 65 or sixty six bytes.
Parameters (secp256k
Standards organizations like the CA/Browser Discussion Board define baseline requirements for supported key sizes and algorithms to keep up belief and interoperability throughout methods. ECC is utilized in both digital signatures through Elliptic Curve DSA (ECDSA), and in key exchange via Elliptic Curve Diffie-Hellman (ECDH). These algorithms are applied in different elements of the SSL standard. First, SSL certificates may be signed with ECDSA instead of RSA. The second use for ECC is during the handshake when the Internet server and client are negotiating session keys that are used to encrypt all of the knowledge sent between the http://hotesib.ru/bestik/7nGvlB9mNk4/Backpack-security-in-hotels-and-hostels-tip.html server and browser.